Arista EOS CVE-2026-7473: still unfixed, and no fix is coming
Arista's tunnel decapsulation flaw has been on CISA's KEV list since June, and Arista says no software fix is planned. Find the exposed switches and fence them with ACLs.

Arista's tunnel decapsulation flaw has been on CISA's KEV list since June, and Arista says no software fix is planned. Find the exposed switches and fence them with ACLs.
A WAF won't fix this autumn's PHP, Java, WordPress or Atlassian flaws, but it can buy time while you patch. What ten major WAF vendors have published for each, where they're silent, and where a WAF can't help at all.
Most attacks that stop a plant start in IT. What the data says about IT-to-OT pivots and purely OT attacks, whether the Purdue model is Over The Top, and whether Nozomi, Claroty and rivals are worth the money.
Since 11 September, manufacturers selling into the EU must report actively exploited vulnerabilities within 24 hours. What the CRA requires, who is caught and what to do.
The year's big security deals, scored: what each did to the buyer's share price, what it means for licence bills, and whether it makes sense. Cisco and Splunk get the long treatment, with Broadcom and VMware as the licensing warning.
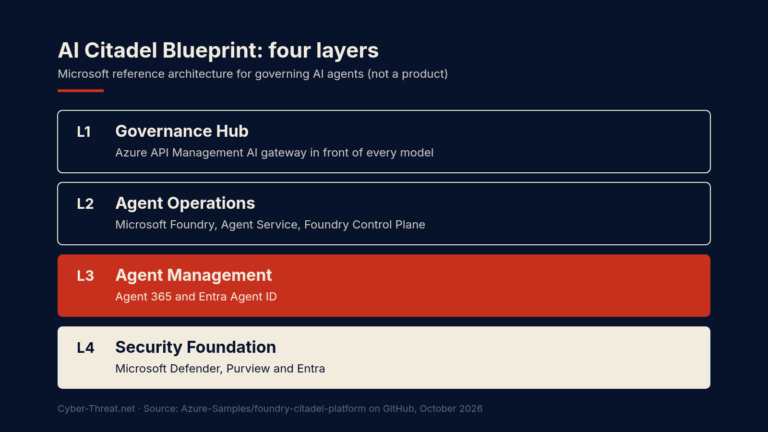
Ignite opens on 17 November. What Microsoft has confirmed about Agent 365, including its free tier, what 'Citadel' actually is, and how Microsoft compares with its rivals' agent-security buying spree.
Some flaws will never get a patch, some don't have one yet, and some have one you can't install. How to find them, fence them, watch them and plan their exit.
A hijacked LiteLLM release pipeline pushed a credential stealer to PyPI and Docker for about two hours on 21 October. Rebuild on 1.106.2 and rotate secrets.